Inside the pack
14 pages, ready to fill in
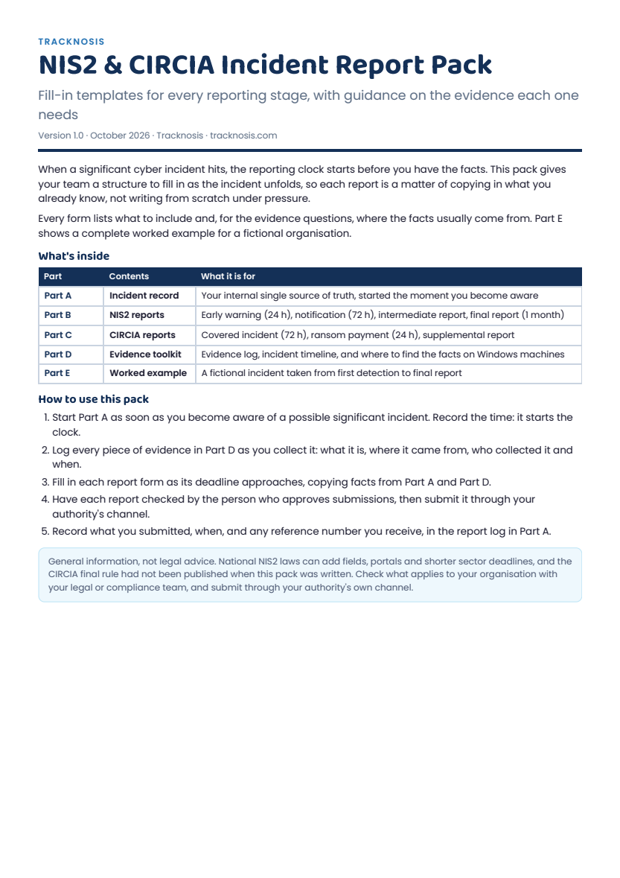
Every form lists what to include and, for the evidence questions, where the facts usually come from. Use the Word file as your working copy and the PDF to review or print.
Fill-in templates for every reporting stage, in Word and PDF, with guidance on the evidence each report needs.
Your report pack is on its way. If it hasn't arrived in a few minutes, check your spam folder.
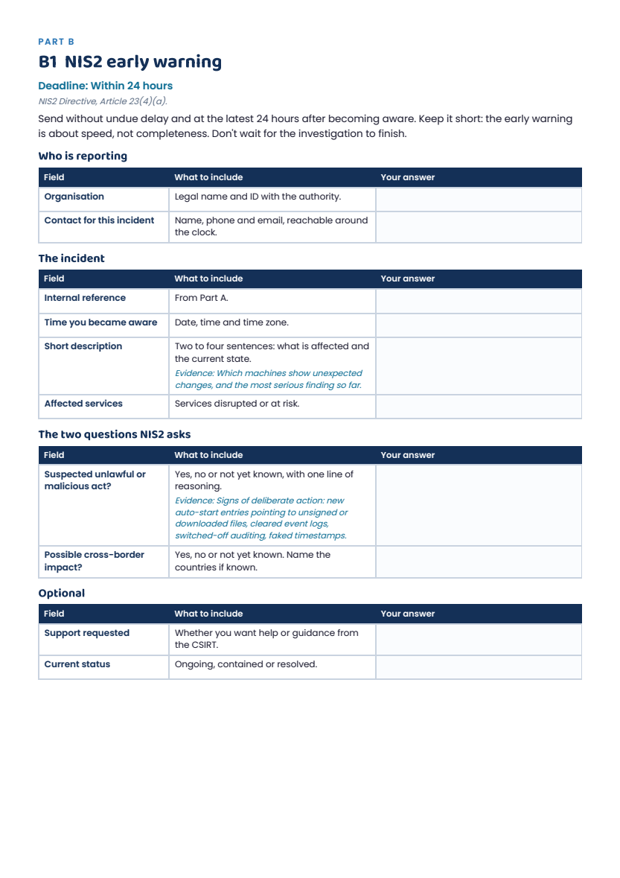
Every form lists what to include and, for the evidence questions, where the facts usually come from. Use the Word file as your working copy and the PDF to review or print.
NIS2 requires essential and important entities to report significant incidents to their national CSIRT or competent authority in stages. The pack has a form for each one.
CIRCIA will require covered US critical infrastructure organisations to report to CISA. The deadlines are set in the law; the final rule confirms who is covered and the exact content.
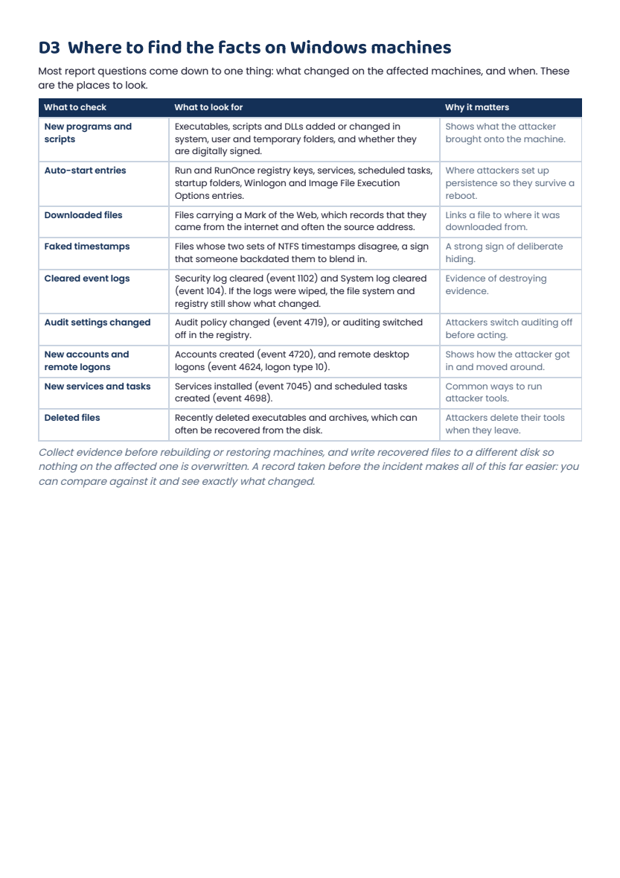
Every report asks the same questions: which systems are affected, is it malicious, what are the indicators of compromise, when did it start, and what was the root cause? Answering them means knowing exactly what changed on your machines. Tracknosis reads every file and registry record directly from the disk, compares each scan with the last, and flags signs of tampering such as cleared logs, so the facts are ready when the clock starts.
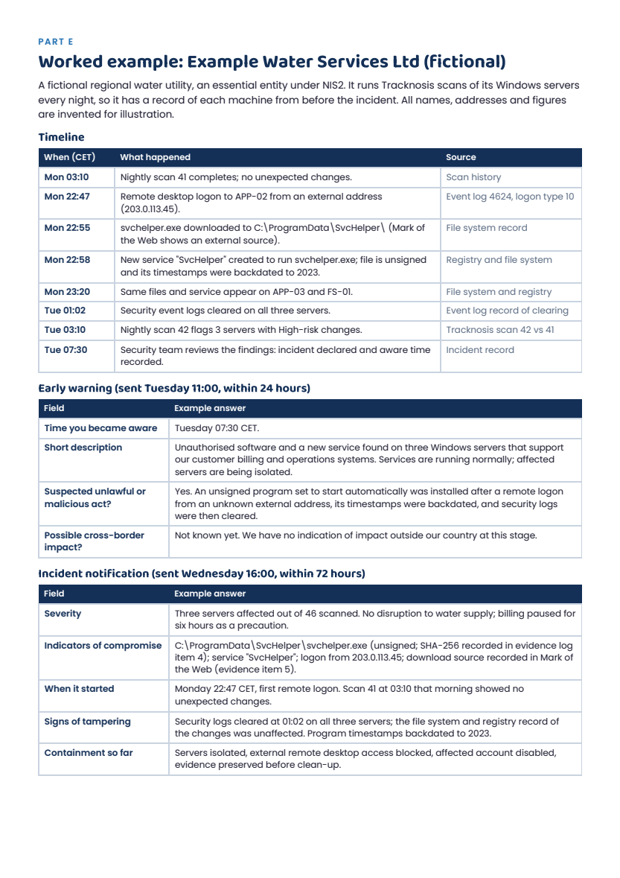
Under Article 23(4)(a) of the NIS2 Directive, the early warning must be sent within 24 hours of becoming aware of a significant incident and say whether the incident is suspected to be caused by unlawful or malicious acts, and whether it could have a cross-border impact. It is meant to be quick, not complete.
The incident notification is due within 72 hours and gives an initial assessment of severity and impact, with indicators of compromise where available. The final report is due within one month of the notification and must include a detailed description, the type of threat or likely root cause, the mitigation measures applied and ongoing, and any cross-border impact.
Each EU country sets its own reporting channel, usually a portal run by the national CSIRT or competent authority, and some add their own fields. A template like this one helps you prepare the content so that submitting it through your national channel is quick.
Under CIRCIA, covered critical infrastructure organisations must report a covered cyber incident to CISA within 72 hours of reasonably believing it occurred, and a ransom payment within 24 hours of making it, with supplemental reports when substantial new information becomes available. The final rule, which sets who is covered and the exact content, was under White House review in October 2026.
Yes. An organisation with operations in both the EU and the US can be required to report the same incident under both regimes, each with its own clock. Keeping one incident record and evidence log, as this pack does, lets you answer both from the same facts.
Yes. Enter your name and email address and we will email you links to the Word template and the PDF.
General information, not legal advice. National NIS2 laws can add fields, portals and shorter sector deadlines. See also: NIS2 & CIRCIA overview · Readiness checklist · What the 24- and 72-hour clocks demand
Templates for every reporting stage, an evidence log, and a worked example. Just your name and email.
Email me the pack