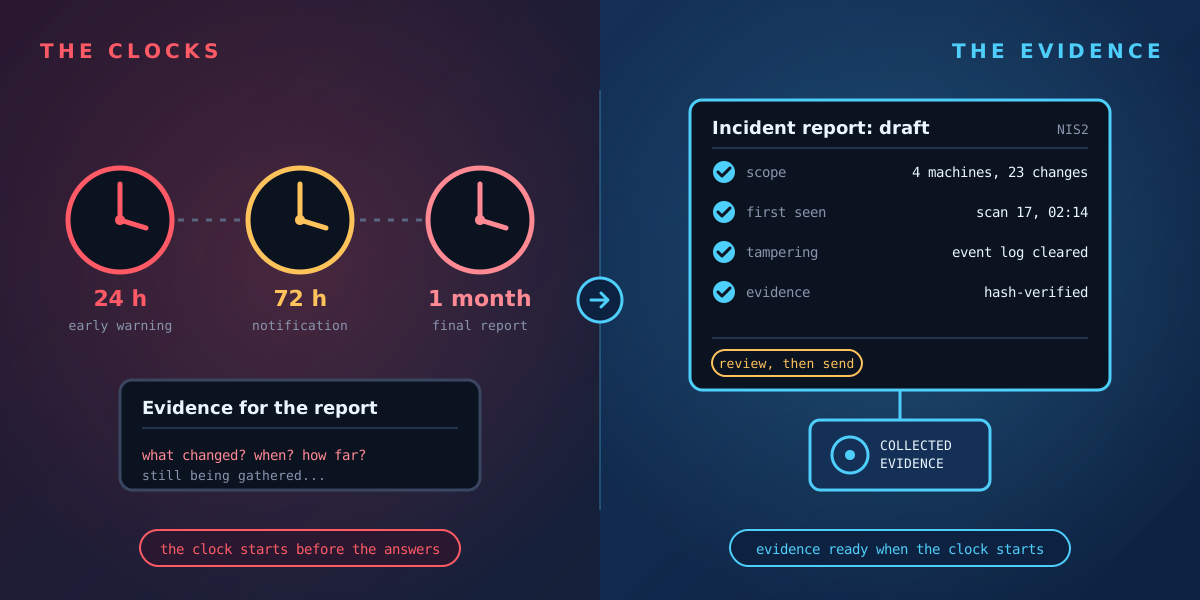
Cyber incident reporting is no longer a courtesy. In Europe, NIS2 makes it a legal duty with strict deadlines. In the US, CIRCIA will do the same for critical infrastructure. Here is what each clock asks for, and what you need to have ready.
This article is general information, not legal advice. Check the rules that apply to your organisation with your legal or compliance team.
NIS2 (EU, in force)
NIS2 applies to medium and large organisations in a wide range of sectors, from energy and health to digital services and manufacturing. For a significant incident it sets three main stages:
- Early warning within 24 hours of becoming aware: is the incident suspected to be malicious, and could it affect other countries?
- Incident notification within 72 hours: an initial assessment, including severity, impact and indicators of compromise where available.
- Final report within one month of the notification: a detailed description, the likely root cause, the measures taken, and any cross-border impact.
NIS2 also puts responsibility on management. Management bodies must approve and oversee cyber risk measures and can be held liable for failures. Fines can reach €10 million or 2% of worldwide turnover for essential entities.
CIRCIA (US, coming soon)
The Cyber Incident Reporting for Critical Infrastructure Act requires covered critical-infrastructure organisations to report:
- a covered cyber incident within 72 hours of reasonably believing it occurred;
- a ransom payment within 24 hours of making it.
The deadlines are set in the law. The final rule, which decides exactly who is covered and what reports must contain, was sent for White House review in October 2026 and takes effect after publication.
Other clocks to know
- UK GDPR: personal data breaches reported to the ICO within 72 hours.
- DORA: EU financial firms send an initial notice within 4 hours of classifying an incident as major.
- UK Cyber Security and Resilience Bill: proposes 24-hour and 72-hour reporting, and is currently in Parliament.
The common problem: evidence
Every one of these reports asks the same underlying questions: what happened, when, what was affected, and what you did about it. The 72-hour report and the final report in particular need facts, not guesses. Teams that struggle usually do so not because they can't write the report, but because they can't establish what actually changed on their systems.
Tracknosis helps with that part. It shows every file and registry change on your Windows machines between scans, flags signs of tampering such as cleared logs, stamps each scan with machine, operator and time, and drafts an incident report from that evidence for your team to review and complete.
Get ready before the clock starts: get our free NIS2 & CIRCIA incident report templates and readiness checklist, or see how Tracknosis helps with NIS2 and CIRCIA.
See what changed on your Windows machines
Tracknosis gives you proactive forensic monitoring and continuous forensic observability for Windows Infrastructure.
Contact Us More articles